News Cloud Security
Datadog Cloud Security Report Shows Fourfold Rise in Vulnerabilities
Datadog's November 2026 report documents a sharp increase in cloud vulnerabilities, widespread use of long-lived AI keys, and rapid adoption of fresh software packages.
Datadog released its State of Cloud Security 2026 report on November 10, 2026. The analysis examined security data from thousands of organizations running workloads on AWS, Azure, and Google Cloud. Median counts of high or critical vulnerabilities per cloud service increased from 4 in February to approximately 16 in November.
Key Metrics from the 2026 Report
The fourfold rise aligns with broader patterns observed across the year. The steepest monthly jump occurred between May and June, coinciding with expanded use of AI security research tools that accelerated vulnerability discovery. More than one in five organizations now consume cloud-hosted AI inference services such as Amazon Bedrock, Azure Foundry, and Google Gemini.
Long-lived AI API keys remain prevalent. Nearly half of Gemini users and 17 percent of Bedrock users continue to rely on them. In Azure environments, 97 percent of organizations have not rotated default long-lived keys. These practices extend the window during which compromised credentials can be exploited.
Cloud workloads contain an average of 149 software packages or dependencies, with over half classified as indirect or transitive. Sixty percent of organizations deploy versions released less than 24 hours earlier, and such fresh packages appear in 21 percent of applications. The report cites Shai-Hulud 2.0 as an example of supply-chain malware that targets cloud credentials, secrets managers, and instance metadata.
Adoption Trends and Recommended Controls
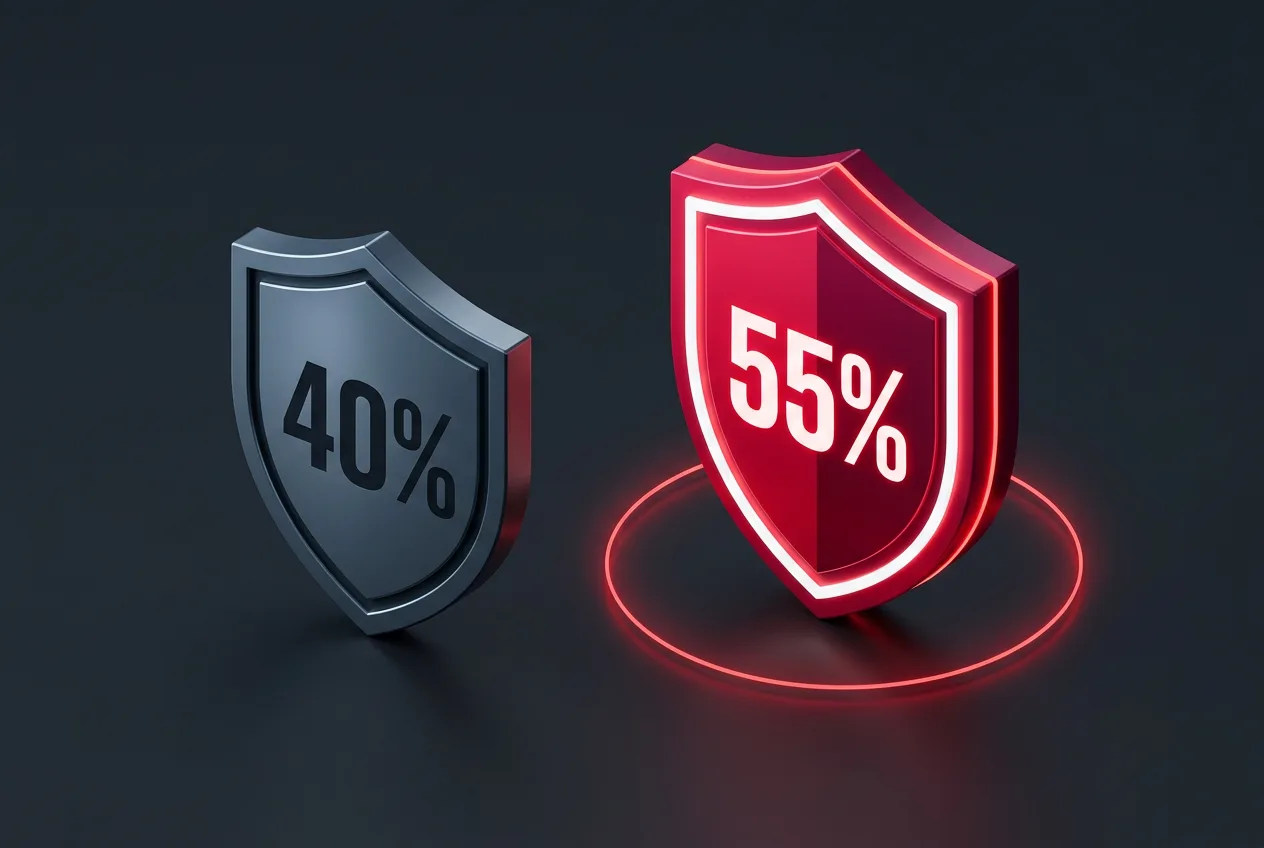
Positive developments include wider use of data perimeters. Fifty-five percent of AWS organizations have implemented these controls, up from 40 percent in 2025. Data perimeters help limit the blast radius of potential breaches by enforcing network and identity boundaries.
The report highlights several practices to reduce exposure. Short-lived identities and keyless pipelines using OIDC reduce reliance on static credentials. Dependency cooldown periods can limit the speed at which newly published packages reach production. Continuous observability across cloud environments provides visibility into runtime behavior and anomalous activity.
These findings reflect the combined effects of accelerated development cycles and increased use of autonomous AI agents. Organizations that maintain strict identity hygiene and slower dependency ingestion appear better positioned to manage the expanded attack surface documented in the report.
Frequently asked questions
What does the Datadog report say about AI API keys?
The report states that nearly 50 percent of Gemini users and 17 percent of Bedrock users rely on long-lived keys, while 97 percent of Azure organizations do not rotate default keys.
How many software packages do cloud workloads typically contain?
Cloud workloads average 149 packages or dependencies, with more than half being indirect or transitive, and many organizations deploy versions released within the previous 24 hours.
What positive trend does the report identify for AWS users?
Fifty-five percent of AWS organizations now use data perimeters, an increase from 40 percent in 2025, to constrain potential breach impact.
Which malware example is mentioned in the supply-chain findings?
Shai-Hulud 2.0 is cited as supply-chain malware that targets cloud credentials, secrets managers, and instance metadata.
Comments 1