News Cybersecurity
CERT-In Crafty Falcon Advisory Warns of AI-Powered Attacks on Financial Firms
India's CERT-In released a critical advisory on November 4, 2026, detailing an active AI-driven campaign by threat actor Crafty Falcon against the BFSI sector.
India's Computer Emergency Response Team issued Critical Advisory CIAD-2026-0058 on November 4, 2026, designating threat actor Crafty Falcon for an ongoing AI-driven campaign against the country's banking, financial services and insurance sector. The advisory, issued through the CSIRT-Fin unit, updates an earlier notice from October 9, 2026, and states that attacks remain active with continued reports of successful intrusions.
Scope of Targets and Attack Patterns
The advisory identifies non-banking financial companies, digital lending platforms, fintech entities, payment aggregators, payment service providers, and cryptocurrency exchanges as primary targets. Attackers focus on abuse of payment and disbursement APIs to execute unauthorized fund transfers, beginning with micro-value test transactions before scaling to larger amounts.
Entry points include internet-exposed non-production environments such as UAT, staging, and testing servers. Once inside, operators move laterally using shared credentials and tokens. They also exploit cloud services including AWS Systems Manager and Lambda functions. Additional methods involve reverse-engineering victim code for custom exploits, bypassing IP allow-lists through third-party fetcher pools, and rapid deployment of payloads against newly disclosed vulnerabilities in PHP and Node.js environments.
Timing of operations often coincides with holidays, weekends, and periods of reduced monitoring. The advisory notes that entities previously targeted after incomplete remediation have faced renewed attempts. No specific victim names, incident counts, or loss figures appear in the advisory or subsequent public reports.
AI Tools and Technical Capabilities
Crafty Falcon operators rely on publicly available AI-driven offensive security tools to automate full attack chains. The listed tools include ARTEX, an LLM-based multi-agent penetration testing and command-and-control platform; PentAGI, an autonomous multi-agent penetration testing system; Cairn, described as an attack search engine; and the CyberStrikeAI framework. These tools allow generation and refinement of tailored scripts at machine speed while adapting payloads in real time.
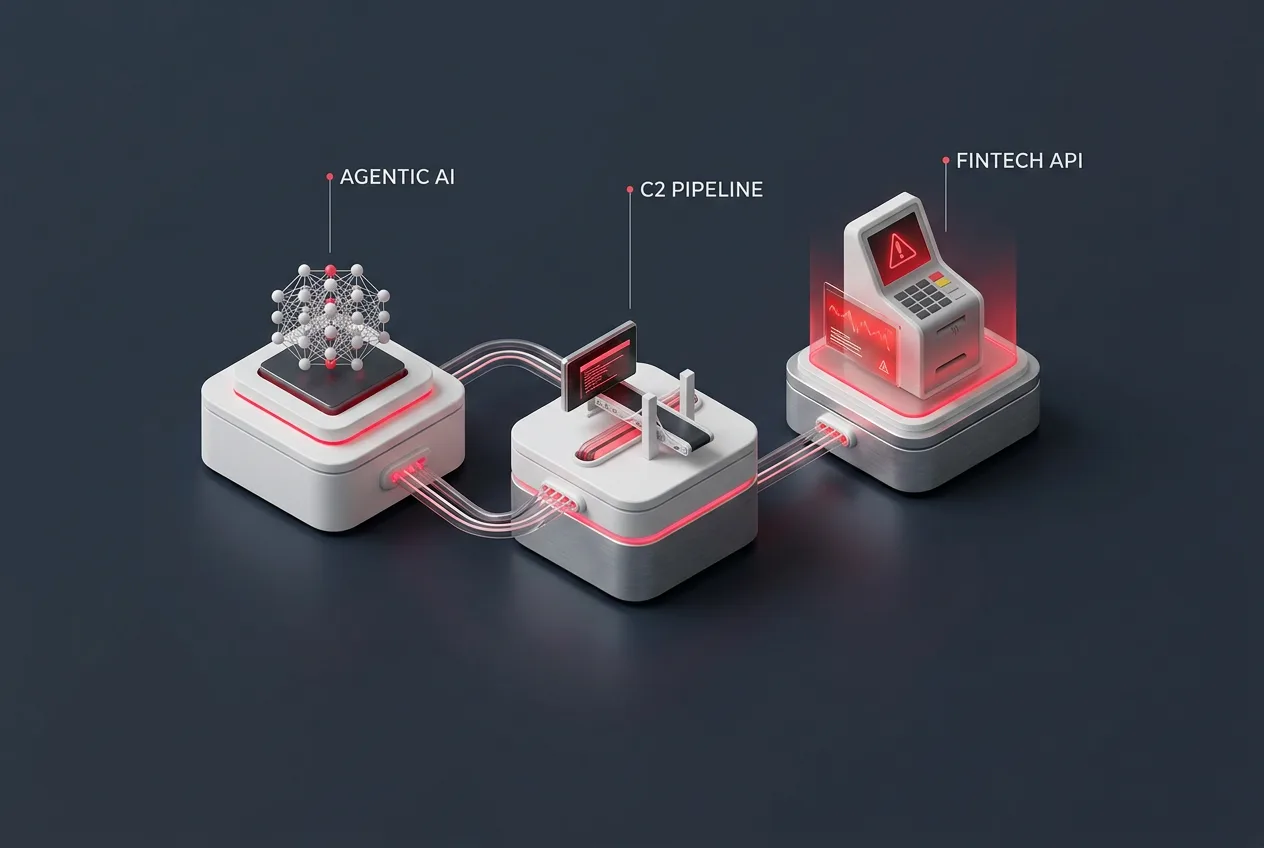
The advisory highlights theft of cryptocurrency wallet keys and subsequent fund siphoning as a recurring objective. It also references prior researcher links between certain tools, including ARTEX, and activity observed against financial institutions in other regions. CERT-In directs all affected entities to maintain 24x7 monitoring, assume persistence after any incident, and conduct full forensic verification before declaring systems clean.
Required Actions and Ongoing Monitoring
BFSI organizations must implement listed technical controls covering cloud log monitoring, environment isolation, API hardening, transaction monitoring for test patterns, and protection of cryptographic keys. Entities are instructed to report incidents promptly to CERT-In and CSIRT-Fin. The advisory emphasizes heightened vigilance during upcoming low-monitoring windows, including the Diwali period.
Further restricted advisories containing indicators of compromise and detection rules are expected as monitoring continues. CERT-In has previously issued related guidance on AI-focused threats, reflecting a pattern of increased attention to automated attack methods in the financial sector.
Frequently asked questions
What is the CERT-In Crafty Falcon advisory about?
The November 4, 2026 advisory CIAD-2026-0058 describes an active AI-powered campaign by the Crafty Falcon threat actor targeting India's BFSI sector through automated tools and API abuse.
Which tools does Crafty Falcon use in the attacks?
The advisory lists ARTEX, PentAGI, Cairn, and the CyberStrikeAI framework as the primary AI-driven tools employed to automate reconnaissance, exploit development, and payload adaptation.
Which organizations face the highest risk from these attacks?
Non-banking financial companies, digital lenders, payment service providers, fintech firms, and cryptocurrency exchanges are explicitly named as targets in the advisory.
What immediate steps does CERT-In recommend?
Organizations must increase 24x7 monitoring, harden APIs, isolate environments, monitor for test transactions, protect crypto keys, and report incidents to CERT-In and CSIRT-Fin.
Comments
No comments yet. Be the first!