News Blockchain
Initia Exploit Forces Layer 1 and Rollups Halt After MoveVM Theft
Initia paused its Layer 1 and all rollups on October 23, 2026, after a MoveVM exploit allowed an attacker to mint unbacked bridged assets worth roughly $2.7 million.
On October 23, 2026, at approximately 14:59 UTC, an attacker exploited a Day-0 bug in Initia’s MoveVM implementation on the Cosmos SDK. The flaw involved script caching that bypassed security checks, allowing the attacker to spoof VM state and mint unbacked bridged tokens equivalent to WETH, iUSD and USDC without changing total supplies or affecting native INIT tokens.
The attacker bridged out roughly $2.7 million in assets through the LayerZero bridge and Noble/CCTP within about seven minutes. The stolen funds included 105 WETH plus around 1.4 million AUSD0 via LayerZero and 1.08 million USDC via Noble/CCTP. The assets were later swapped into approximately 1,135.52 ETH held at Ethereum address 0x358ef0130f7a5aa516dcd81bdc80b18cde41cac8.
Timeline of the Initia Exploit and Network Response
Initia halted block production on its Layer 1 and all rollups at 15:41:30 UTC, roughly 42 minutes after the unauthorized mint and 14 minutes after researcher Spreek issued a public alert. The pause stopped both transaction processing and bridging activity across the network. Co-founder Zon, identified as Ezaan Mangalji, stated that the issue was specific to the MoveVM and did not affect native INIT tokens.
Agora, the issuer of AUSD, clarified that no Agora-issued AUSD was minted on Initia. The loss instead affected third-party bridged AUSD adapters and depositors. On October 24, Initia published additional details confirming the script-caching flaw and announced that asset recovery efforts had begun with security partners. A security fix and subsequent audit were scheduled for completion within days, though the network remained paused pending a full post-mortem.
As of October 25, 2026, no restart date, final loss confirmation or complete post-mortem report had been released. Several exchanges, including Kraken, paused deposits and withdrawals involving Initia-related assets while the investigation continued.
Background on Initia Architecture and Bridge Mechanics
Initia operates as a Cosmos SDK-based Layer 1 designed to interconnect multiple rollups, referred to as Minitias. The exploit targeted bridge mechanics in which Ethereum-side adapters accepted valid messages that originated from unbacked mints executed on the Initia side. This allowed the attacker to create tokens on Initia that could be redeemed for assets on external chains without corresponding collateral.
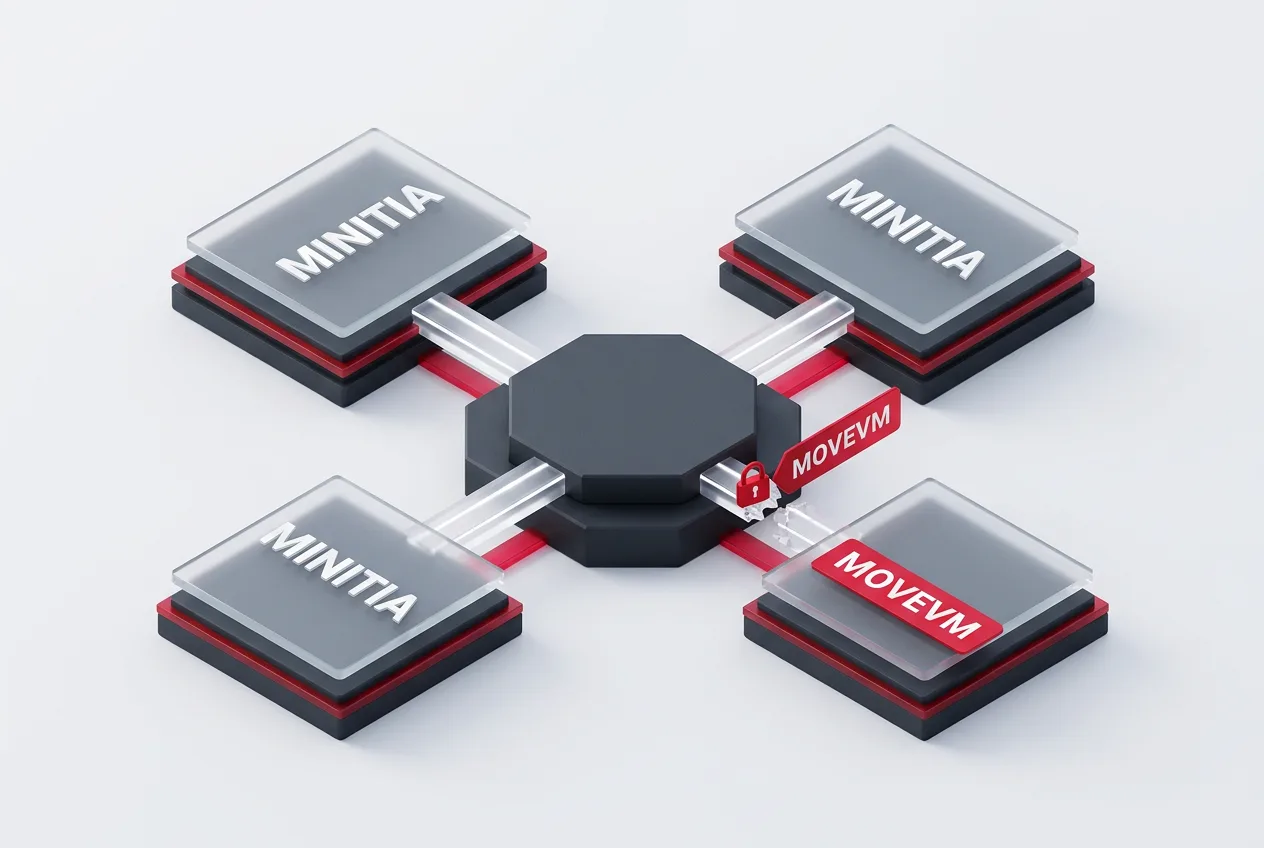
The MoveVM on Initia had not previously encountered this class of caching vulnerability in production. The incident highlighted differences between standard Cosmos SDK token handling and the custom bridging logic required for cross-chain assets. No native Initia tokens or on-chain supplies of INIT were altered during the attack.
Security researchers noted that the rapid response by the team limited further damage after the initial mint. The decision to halt the network prevented additional bridged outflows once the flaw became public. Recovery efforts now focus on tracing the 1,135.52 ETH and coordinating with counterparties on the affected bridges.
Current Status and Recovery Outlook
Initia has stated that a patched version of the MoveVM will undergo external audit before any resumption of block production. The team continues to work with security firms on tracing the stolen funds and exploring possible recovery paths, though outcomes remain uncertain at this stage. Exchanges that paused trading pairs have not announced reopening timelines.
Users and liquidity providers on third-party bridged assets are advised to monitor official Initia communications for updates on the post-mortem and any compensation mechanisms. The network remains fully paused as of the latest statements on October 25.
Frequently asked questions
What caused the Initia exploit on October 23?
A Day-0 script caching bug in the MoveVM allowed an attacker to bypass checks and mint unbacked bridged tokens. The flaw was specific to Initia’s implementation on the Cosmos SDK.
How much was lost in the Initia exploit?
The attacker bridged out approximately $2.7 million in assets, primarily through the LayerZero bridge and Noble/CCTP. The funds were converted to roughly 1,135 ETH on Ethereum.
Why did Initia halt its Layer 1 and rollups?
The network was paused at 15:41 UTC on October 23 to stop further block production and bridging after the unauthorized mint. The halt remains in place pending a security fix and post-mortem.
Has Initia recovered any funds from the exploit?
Recovery efforts are ongoing with security partners as of October 25. No successful recovery has been confirmed, and the network stays paused until a patched version passes audit.
Comments
No comments yet. Be the first!