News Microsoft
Microsoft Patch Tuesday November 2026 Addresses 1,094 Vulnerabilities With Outlook Zero-Day Fix
Microsoft released its November 2026 Patch Tuesday updates on November 10, addressing roughly 1,094 vulnerabilities across multiple products and fixing an actively exploited Outlook zero-day.
Microsoft released its November 2026 Patch Tuesday updates on November 10, addressing approximately 1,094 vulnerabilities across Windows, Office, Exchange Server, SQL Server, SharePoint, Azure and other products. The release includes 63 to 66 flaws rated Critical, most of which allow remote code execution, along with one actively exploited zero-day in Outlook.
Outlook Zero-Day CVE-2026-124194 Receives Immediate Patch
The zero-day, tracked as CVE-2026-124194, is a spoofing vulnerability in Microsoft Outlook with a CVSS score of 6.5. Attackers can send a specially crafted message file that causes Outlook to connect to an attacker-controlled server without displaying the usual external content warning. This action leaks the user’s NTLMv2 hash, which can then be used for impersonation or offline cracking attempts. The Preview Pane is not an attack vector, and the exploit requires user interaction plus network connectivity.
Microsoft stated the flaw was not publicly disclosed before the patch and confirmed active exploitation in the wild. The update applies to Microsoft 365 Apps for Enterprise and Office LTSC 2021 and 2024 releases, delivered through specific Office update channels rather than Windows cumulative updates alone. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on November 10 and set a November 24 remediation deadline for federal agencies.
Additional high-severity issues in the release include remote code execution flaws in Exchange Server and Windows LDAP components. Elevation of privilege vulnerabilities form the largest category of fixes. No other zero-days or publicly disclosed flaws were included in this batch.
Release Volume and Product Coverage
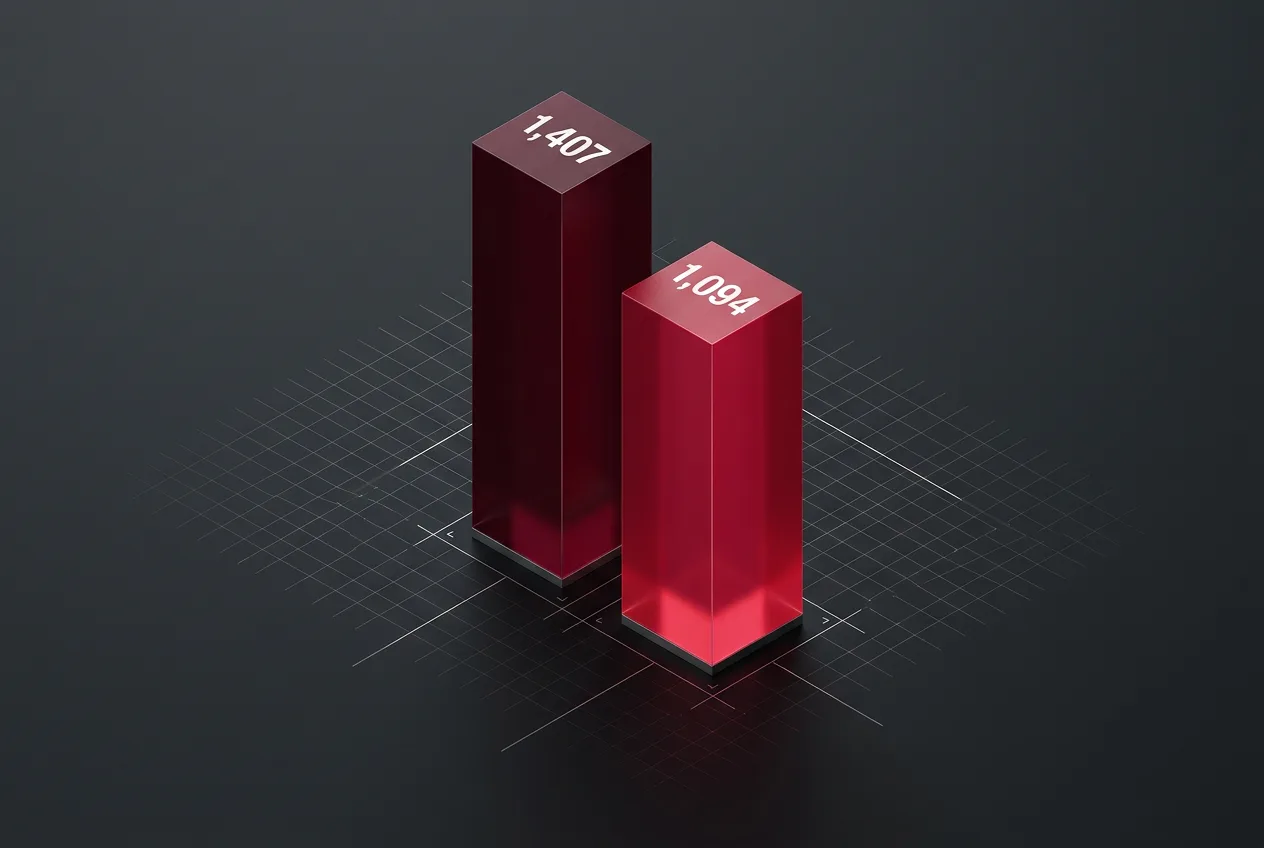
The November total continues a pattern of elevated monthly counts seen earlier in 2026, with October having reached roughly 1,407 vulnerabilities. Microsoft attributes part of the increase to expanded use of AI-assisted discovery tools during internal testing. Some editions of Windows 11 23H2 receive their final security updates as part of this cycle.
Windows cumulative updates such as KB5132061 cover the majority of operating system fixes for Windows 11 24H2, 25H2 and 26H2 versions. Separate patches address Exchange Server, SQL Server, SharePoint and various Azure services. Organizations running mixed environments must verify that both Office and Windows update channels are applied in the correct sequence.
Deployment Priorities for Administrators
Security teams should install the Outlook-specific Office updates first because of confirmed exploitation. Windows cumulative updates follow, with attention to the listed KB numbers for each supported version. Microsoft publishes detailed build numbers for LTSC 2021 and 2024 releases to simplify verification in enterprise deployments.
Federal agencies must meet the November 24 CISA deadline. Broader enterprise and consumer users are advised to apply patches during their next scheduled maintenance window to reduce exposure. Post-release monitoring continues for any compatibility issues or additional exploitation reports.
Frequently asked questions
When was the November 2026 Patch Tuesday released?
Microsoft published the updates on November 10, 2026. The release covers roughly 1,094 CVEs across multiple product lines.
Which Outlook versions receive the CVE-2026-124194 fix?
The patch applies to Microsoft 365 Apps for Enterprise and Office LTSC 2021 and 2024. Specific builds are listed in the Microsoft advisory for each edition.
How many critical flaws were included this month?
Microsoft rated 63 to 66 vulnerabilities as Critical. Most allow remote code execution when successfully exploited.
What action should organizations take first?
Priority goes to the Office updates that address the exploited Outlook zero-day. Windows cumulative updates should follow immediately afterward.
Comments
No comments yet. Be the first!