News Cybersecurity
SonicWall CVE-2026-19868 Patches Fix SonicOS SSLVPN SAML Bypass Flaw
SonicWall disclosed CVE-2026-19868 on November 6, 2026, and issued patches for a high-severity authentication flaw in SonicOS that affects SAML-protected SSL VPN logins.
SonicWall disclosed CVE-2026-19868 on November 6, 2026, in security advisory SNWLID-2026-0014. The high-severity flaw allows bypass of SAML authentication controls, including enforced MFA, on SonicOS SSL VPN services when alternate login methods such as local, LDAP, or RADIUS remain available.
The company urged immediate upgrades after investigating reports of active exploitation. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog the same day, setting a November 20, 2026, remediation deadline for federal civilian agencies.
SonicWall CVE-2026-19868 Technical Details and Affected Versions
The vulnerability carries a CVSS score of 7.1 according to SonicWall and 7.5 from CISA-ADP and NVD. It is classified under CWE-308 and stems from insufficient authentication enforcement. Attackers with valid credentials for a non-SAML method can access the SSL VPN portal while bypassing SAML-based MFA and other controls. No workarounds exist.
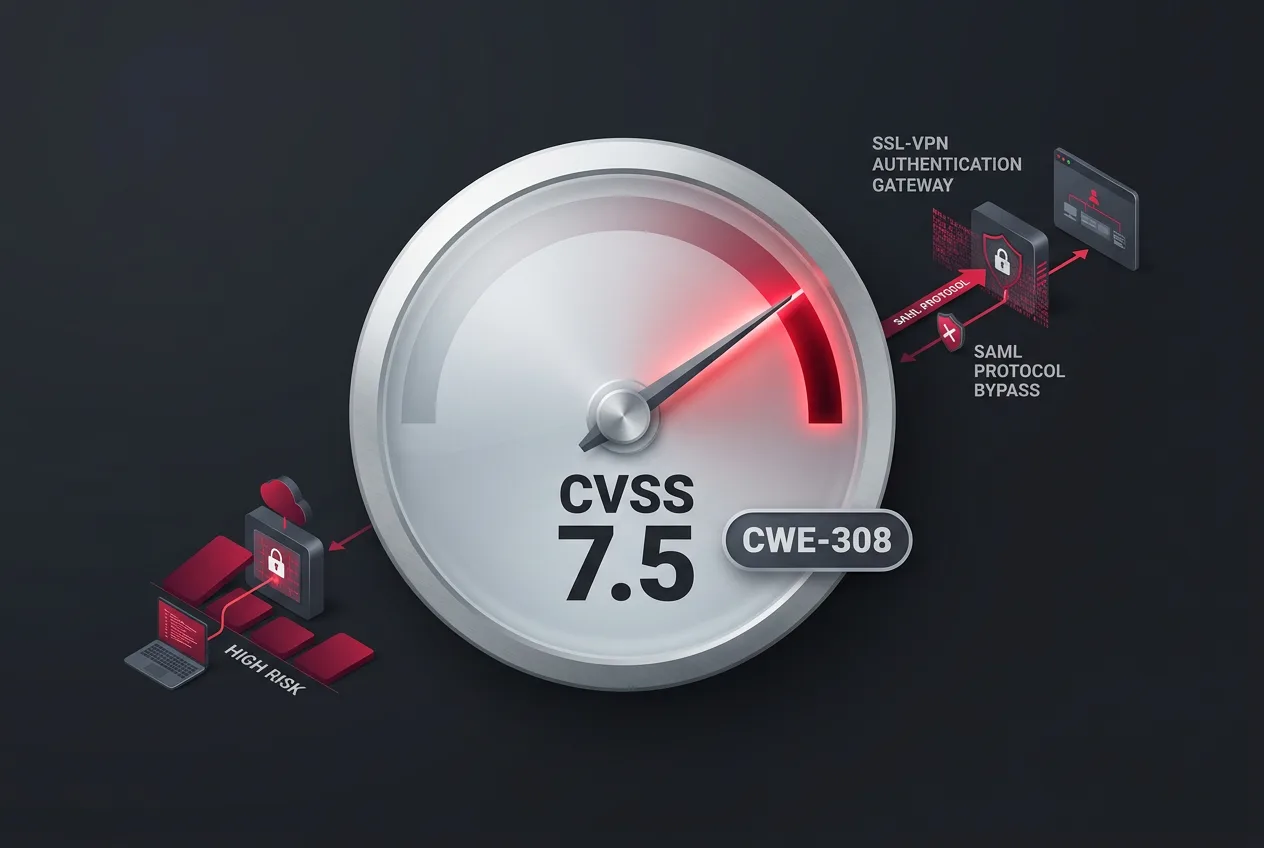
Affected products include Gen7 firewalls and NSv virtual appliances running SonicOS 7.3.3-7015 and earlier versions. Gen8 devices on 8.2.2-8015 and prior builds are also impacted. SonicOS 7.3.4-7013 became available around October 20, 2026, with 7.3.4-7015 following on November 5. The Gen8 fix in version 8.2.3-8015 shipped on November 6, 2026. Gen6 and older platforms reached end of support and receive no updates.
The issue was reported by Ryan Harris of The Electronic Office. It formed part of a larger advisory that also covered separate management interface and SSL VPN weaknesses. SonicWall PSIRT confirmed exploitation attempts prior to the public disclosure.
CISA KEV Addition and Immediate Response Steps
CISA listed CVE-2026-19868 in the KEV catalog on November 6, 2026, under BOD 26-04 requirements. The entry notes ransomware use as unknown at the time of cataloging. Organizations running exposed SonicOS SSL VPN instances with SAML enabled face the highest risk.
Administrators should first inventory all deployed firewalls and virtual appliances to identify running SonicOS versions. Next, verify whether SAML authentication is active for any SSL VPN policies. Devices on the listed vulnerable builds require prompt upgrade to the fixed releases. Canadian Centre for Cyber Security and other agencies have echoed the call for rapid remediation.
Broader context includes repeated focus on authentication bypass issues across VPN products in recent years. The addition to KEV signals that federal agencies and regulated entities must treat the flaw with priority. Tracking vendor release notes for any follow-on patches remains necessary as further details emerge.
Frequently asked questions
Which SonicOS versions receive fixes for CVE-2026-19868?
SonicOS 7.3.4-7013 and 7.3.4-7015 address the issue on Gen7 devices. Version 8.2.3-8015 fixes it on Gen8 platforms. Earlier builds remain vulnerable.
Does CVE-2026-19868 affect all SonicWall firewalls?
Only Gen7 and Gen8 models with SonicOS versions at or below the listed thresholds are impacted. Gen6 and older hardware reached end of support and receives no patches.
Why was CVE-2026-19868 added to the CISA KEV catalog?
CISA confirmed active exploitation and assigned a November 20, 2026, deadline for federal civilian agencies under BOD 26-04. The entry covers the SAML bypass in SonicOS SSL VPN.
What authentication methods allow bypass under the flaw?
Users with valid local, LDAP, or RADIUS credentials can circumvent SAML controls when those methods remain enabled alongside SAML for SSL VPN access.
Comments 4