News Cryptocurrency
Qubic Blockchain Halts Network After Wallet Theft Exploiting Weak Seed Generation
Qubic blockchain stopped its mainnet on October 18, 2026, after an attacker stole roughly $1.3 million in QU tokens from 1404 wallets through predictable seed generation.
On October 17 and 18, 2026, the Qubic blockchain halted its mainnet after an attacker drained 1,404 wallets by exploiting weak, predictable 55-character seeds generated with insufficient randomness. The incident resulted in the theft of approximately 2.94 trillion QU tokens, valued at about $1.3 million at the time of the attack.
Timeline of the Attack and Network Halt
The exploit unfolded over roughly 104 minutes, beginning at 23:42 UTC on October 17 and ending at 01:26 UTC on October 18. Qubic validators, known as Computors, identified the ongoing drain and paused the network at tick 85,371,949 early on October 18. At the moment of the halt, 87.1 percent of the stolen QU tokens, or about 2.56 trillion, remained immobilized on-chain. The remaining 12.9 percent reached the MEXC exchange, where the receiving account was frozen within approximately one hour. Current reports indicate that 100 percent of the stolen funds stay inaccessible to the attacker.
The Qubic network uses a fee-less Layer-1 design based on Useful Proof of Work for decentralized AI and compute tasks. The pause affected all on-chain activity, including transfers, while staking through QEARN remained unaffected. No mainnet restart date has been announced as of October 19.
Root Cause and Scope of the Seed Vulnerability
The flaw originated in the wallet seed generation process, not in the Qubic protocol itself. Affected seeds were created before October 18, 2026, using JavaScript Math.random() in browser environments on iPhone, iPad, Safari on Mac, or the Qubic iOS app prior to the July 2025 update. The attacker reproduced the seeds offline by precomputing possible values. Qubic released wallet version 4.26.4 on October 18, replacing the insecure random function with crypto.getRandomValues() to ensure stronger entropy.
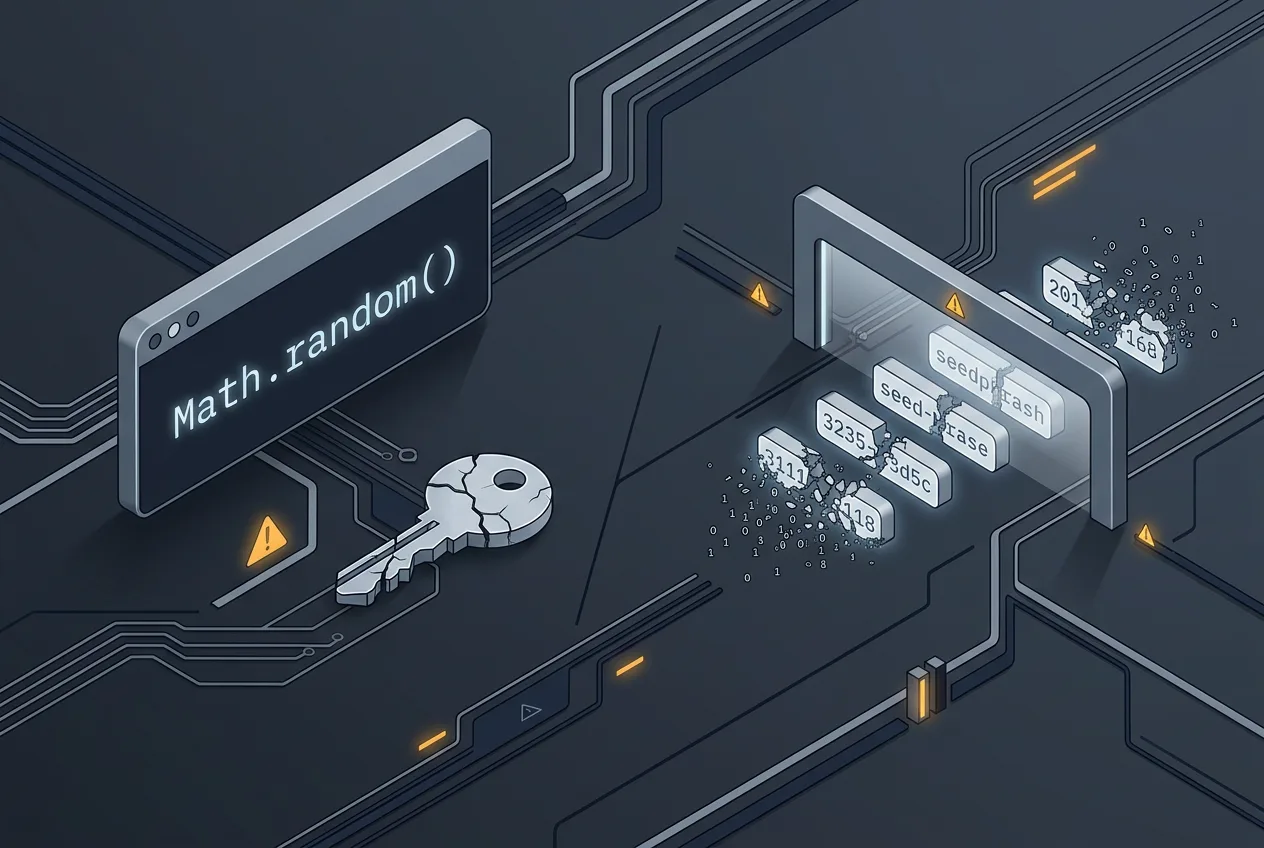
The issue was limited to client-side seed creation. Core protocol operations and existing validator infrastructure were not compromised. The team identified additional vulnerable wallets and secured those funds before further losses occurred. Exchanges including MEXC and Bitget suspended QUBIC deposits and withdrawals following the incident.
Recovery Actions and Planned Next Steps
Qubic confirmed the seed-generation issue and the network halt through an official statement on X. The team stated that contained funds will be addressed through established Computor quorum procedures. As of October 19, the core team continues to map affected wallets and prepare recovery options for a formal vote. A full technical report is expected once the plan is settled.
Affected users have been advised to update to the latest wallet version and to file reports with local law enforcement. The network remains paused while validators finalize the recovery framework. No additional unauthorized movements have been recorded since the initial halt.
Frequently asked questions
What caused the Qubic wallet theft?
The theft resulted from weak, predictable seeds generated with JavaScript Math.random() in certain browser and app environments. Attackers precomputed the seeds offline and accessed 1404 wallets containing roughly 2.94 trillion QU tokens.
When did Qubic halt its network?
Validators paused the mainnet at tick 85,371,949 early on October 18, 2026, after detecting drains that began the previous evening at 23:42 UTC.
Are the stolen funds still accessible to the attacker?
No. 87.1 percent of the tokens remain frozen on-chain due to the network halt, and the remaining portion was frozen by MEXC shortly after deposit. All stolen funds are currently inaccessible.
What fixes has Qubic released?
Wallet version 4.26.4, issued on October 18, replaces Math.random() with crypto.getRandomValues(). The team has also secured additional vulnerable wallets and suspended deposits on major exchanges.
Comments 1