News Cryptocurrency
Cysic Bridge Exploit Allows Unauthorized Mint of 10 Million CYS Tokens
Cysic suspended its cross-chain bridge on October 17, 2026, after an attacker minted 10 million unauthorized CYS tokens on BNB Smart Chain and moved proceeds worth roughly $727,000 to Ethereum.
On October 17, 2026, at 12:31:38 UTC, an attacker exploited Cysic’s cross-chain bridge to mint 10,000,000 CYS tokens on BNB Smart Chain. The recipient address was 0xA4e1827Fe2664fD0797a55e442b2e2639449C255. Cysic Foundation suspended the bridge the same day as a containment step, and cross-chain services remain unavailable.
Details of the Cysic Bridge Exploit
The attacker sold approximately 7.2 million CYS tokens through decentralized exchange swaps before the blacklist took effect. Roughly 5.65 million tokens were exchanged for about 588,000 USDT, and 1.55 million tokens yielded around 220 BNB. The attacker then bridged proceeds valued at roughly 306.6 ETH, or $727,000, to Ethereum using Mayan, deBridge, and SWFT protocols.
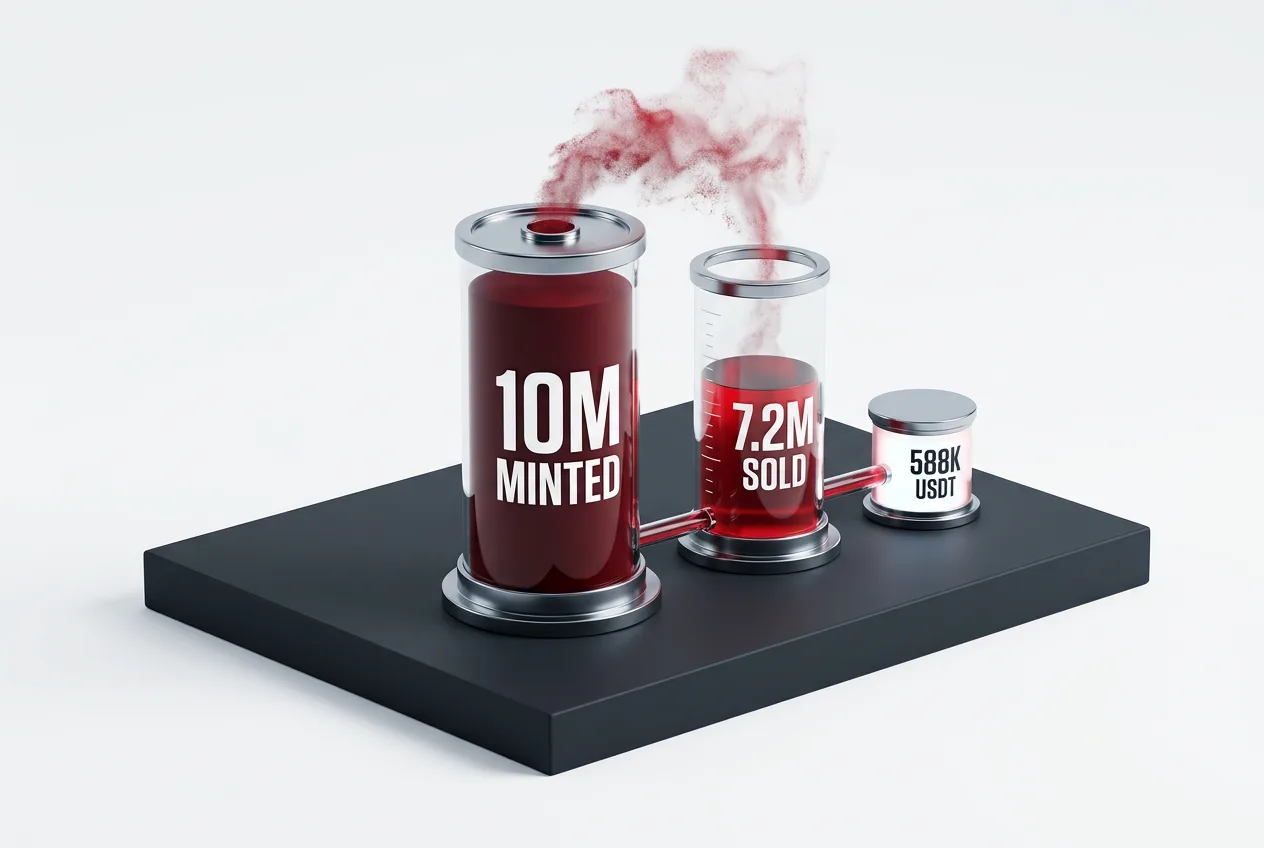
At 13:47:52 UTC, about 76 minutes after the mint, Cysic blacklisted the recipient address in the CYS token contract on BNB Smart Chain. This action froze the remaining 2.8 million tokens. Preliminary analysis indicates the attacker obtained unauthorized database access tied to the bridge and exploited a vulnerability in message-processing logic to submit a fraudulent mint message. The full attack path remains under investigation by Cysic and an external security firm.
The incident affected only the bridge message-processing and minting functions. Cysic mainnet operations, other systems, and existing user wallet assets stayed untouched. The 10 million minted tokens represent roughly 1 percent of total supply, though the exact loss amount depends on final review of token movements and swaps.
Response Measures and Investigation Status
Cysic Foundation immediately halted bridge operations after detecting the unauthorized mint. The team engaged an unnamed professional security firm to investigate the incident, trace funds, and review overall security posture. A follow-up report is planned once the review concludes.
Blacklisting the attacker address limited further on-chain movement of the remaining tokens. No confirmed timeline exists for reopening the bridge. Cysic stated that existing user funds outside the bridge remain secure and unaffected by the exploit.
Market observers continue to monitor on-chain activity linked to the recipient address and the bridged Ethereum funds. Exchanges and liquidity providers that received swapped tokens have not issued public statements regarding any additional controls at this stage.
Market Context and Ongoing Monitoring
Cysic operates a cross-chain bridge that supports token transfers between networks. The October 17 incident marks the first reported security event tied to its bridge infrastructure. Similar bridge exploits have occurred in other projects, often prompting extended service pauses and third-party audits.
Users holding CYS tokens on BNB Smart Chain or other supported chains can continue normal transfers within single-network environments. Cross-chain functionality will stay disabled until Cysic completes remediation and publishes updated security findings.
Industry participants await the external firm’s report for clarity on the message-processing flaw and any recommended protocol changes. Cysic has not disclosed additional technical details beyond the initial incident summary.
Frequently asked questions
What happened during the Cysic bridge exploit?
An attacker gained database access and submitted a fraudulent message to mint 10 million CYS tokens on BNB Smart Chain. Cysic suspended the bridge and later blacklisted the recipient address.
How much value did the attacker move off-chain?
The attacker swapped roughly 7.2 million CYS tokens for about 588,000 USDT and 220 BNB, then bridged proceeds worth approximately 306.6 ETH or $727,000 to Ethereum.
Is the Cysic mainnet affected by the exploit?
No. The incident was limited to bridge message processing and minting functions. Mainnet operations and user wallet assets outside the bridge remain unaffected.
When will the Cysic bridge reopen?
Cysic has not provided a reopening timeline. The bridge stays suspended while an external security firm investigates the root cause and reviews security measures.
What steps has Cysic taken after the exploit?
Cysic suspended the bridge, blacklisted the attacker address, engaged a security firm to trace funds, and plans to issue a follow-up report once the review concludes.
Comments
No comments yet. Be the first!